> For the complete documentation index, see [llms.txt](https://docs.bsure.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.bsure.io/v1/technical-description/security.md).
# Security
To ensure confidentiality and privacy, our application has these features:
* All data is encrypted at rest and in transit.
* No inbound connectivity to the Managed Application.
* Outbound to customer storage only (exception, billable user count goes to MS Billing API) .
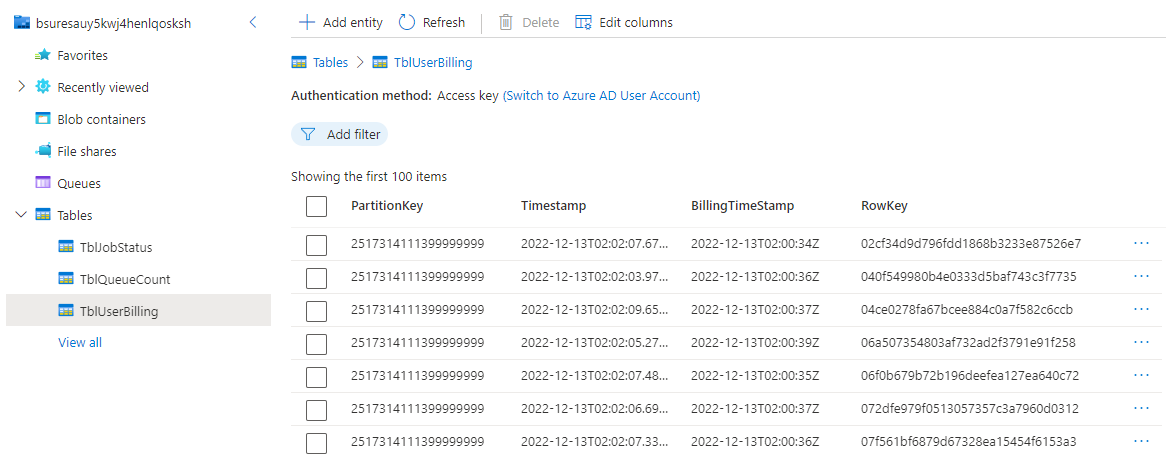
* Information used for billing (user object id) is salted and hashed and stored in a Storage Account in the Managed Resource Group.
* The Managed Application uses [Managed Identity](/v1/technical-description/permissions-required.md#managed-identity-that-holds-these-permissions) to access MS Graph with read only.
* Azure Keyvault for secrets (Bsure personnel cannot access these secrets). The connection string to the Storage Account (provided by you - BYOSA[^1]) where user data is stored.
### Examples
#### Example showing how the billing information is salted and hashed:
#### Example Bsure personnel accessing the Key Vault:
The Keyvault resides in the Managed Resource Group, but Bsure have no access to access the secrets.
Bsure have the Contributor RBAC role, which is not sufficient to read secrets, or elevate permission.
**References:**
Azure built-in RBAC roles:
Azure built-in roles for Key Vault data plane operations:
[^1]: Bring Your Own Storage Account
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://docs.bsure.io/v1/technical-description/security.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.